THREAD 01
Agent Architectures
How autonomous systems plan, preserve state, recover from failure, and remain inspectable over long-running work.
Open question
Which architectural choices make an agent reliable without making it too rigid?
How we investigate
Architecture teardowns, failure analysis, trace inspection, and reproducible design notes.
 4 min read
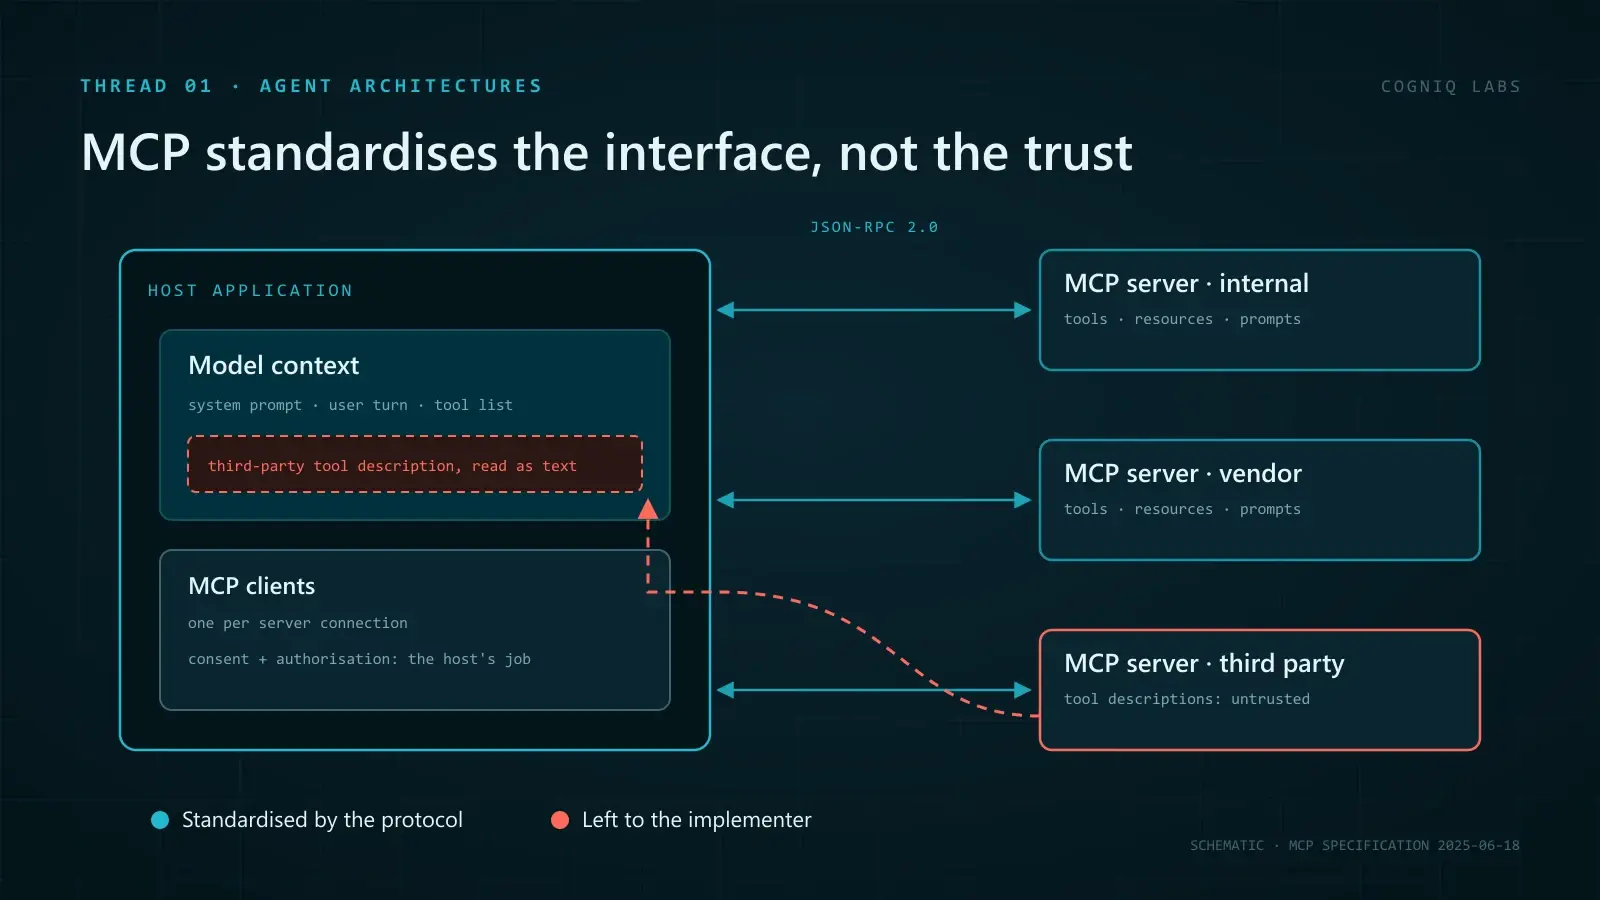
MCP Standardises the Interface, Not the Trust
The Model Context Protocol gives agents one way to reach every tool. Its own specification says it cannot enforce security. What that leaves to you.
Agent ArchitecturesRead 4 min read
Why Multi-Agent Consensus Collapses into Hallucination
Without deterministic grounding, agent debate loops converge on shared falsehoods rather than truth. Here is the mechanism and how to anchor it.
AgentsRead 3 min read
The Hidden Latency Cost of Stateful Multi-Agent Loops
How context growth and sequential model calls make multi-agent systems slower—and how to decide when extra roles are worth it.
Agent ArchitecturesRead 5 min read
Prompt Injection Is Not a Filtering Problem
Published defences report low attack success rates on static benchmarks and fall over against adaptive attackers. What survives that is architecture.
AI securityRead 5 min read
Why AI Security Frameworks Fail in Practice
Frameworks describe controls for a system with a boundary. LLM applications dissolve that boundary, and the checklist stays green while the gap opens.
AI securityRead 5 min read
Most Agent Failures Never Throw an Error
An agent that crashes is the cheap case. The expensive failures return a confident, well-formed, wrong answer, and nothing in the stack notices.
Autonomous AI AgentsRead 3 min read
The Legibility Problem in Autonomous Agents
An autonomous agent is governable only when operators can reconstruct its goals, evidence, decisions, actions, and uncertainty.
Agent ArchitecturesRead